Handala, an Iran-linked hacking group, claims it accessed systems tied to California Water Service and exfiltrated about 5 GB of data from Bakersfield, Visalia and Chico. Cal Water says it is investigating with state and federal partners and reports no known operational disruptions to water or wastewater systems. Independent analysis indicates the intrusion likely affected a billing database and an internal GPS-monitoring tool—not water treatment or distribution controls. U.S. Central Command said it was looking into related reports of strikes near the Strait of Hormuz.
Iran-Linked Hackers Claim Breach Of California Water Utility — Cal Water Investigating, No Disruptions Reported
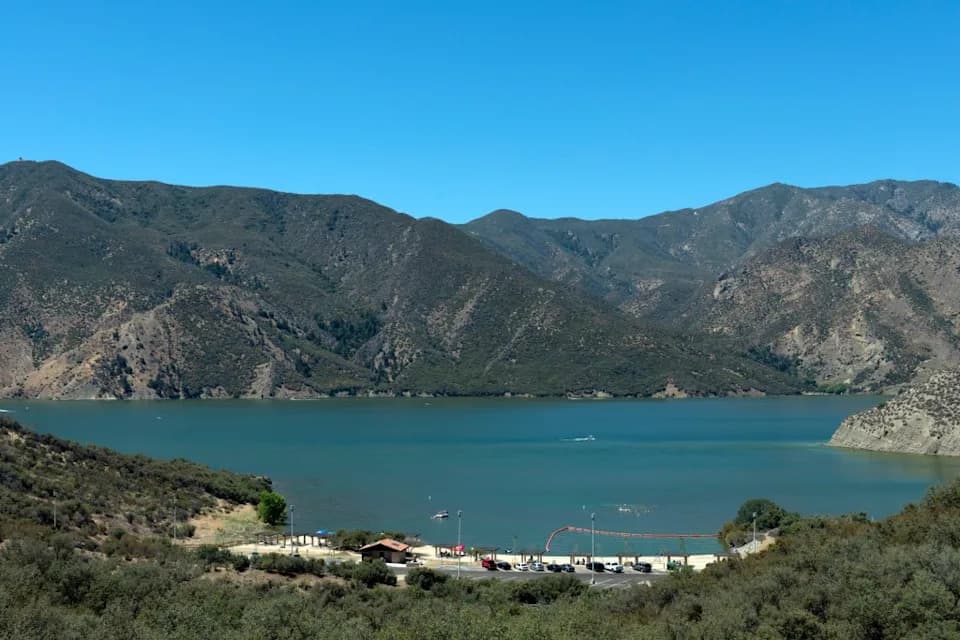
Pyramid Lake, a reservoir formed by Pyramid Dam on Piru Creek in the eastern San Emigdio Mountains, near Castaic, Southern California.
An Iran-linked hacking collective calling itself Handala says it breached systems tied to California Water Service (Cal Water) and exfiltrated roughly 5 gigabytes of internal data. Cal Water has opened an investigation with state and federal partners and says there is no evidence that water treatment or delivery systems have been disrupted.
What Happened
Handala told Iran-aligned Press TV it accessed systems connected to Cal Water and provided screenshots of customer billing records and internal dashboards. The group said the data came from operations in Bakersfield, Visalia and Chico and described the intrusion as retaliation for recent U.S. strikes on Iranian water infrastructure.
"We could have easily cut off the water to American cities," Handala told Press TV, but the group said it refrained from disrupting supplies and framed the action as a warning to Washington.
What Officials Say
Cal Water said it is "working around the clock to investigate" the group's claims with state and federal partners and that no services have been affected. Spokesperson Yvonne Kingman told nonprofit SJV Water that preliminary findings show "no known operational disruptions to our water and wastewater systems, including the billing platform." The utility says its investigation is ongoing.
The U.S. Central Command acknowledged reports of strikes near the Strait of Hormuz and said it was looking into related accounts. Iranian state media reported that U.S. airstrikes recently destroyed a drinking-water facility near the Strait of Hormuz.
Independent Analysis
Cybersecurity firm Dataminr and other independent analysts say available evidence points to a compromise of non-critical IT systems, including a customer billing database (containing names, service addresses, phone numbers, account numbers and payment history) and an internal GPS-based system used for infrastructure monitoring. Analysts emphasize that neither system directly controls water treatment processes or distribution networks.
Dataminr noted that Handala has previously focused on data exfiltration, disruptive malware (wipers) and psychological operations rather than confirmed tampering with treatment chemistry or distribution controls. Cal Water continues to work with partners to determine the full scope and impact of any access.
Why This Matters
Targeting of water-sector IT systems raises public concern because of the potential for broader disruption and psychological impact, even when operational control systems are not accessed. Officials stress the importance of ongoing vigilance, rapid incident response and robust cyber protections for critical infrastructure.
Status: Investigation ongoing. No confirmed operational impacts to water treatment or distribution at this time.
Help us improve.