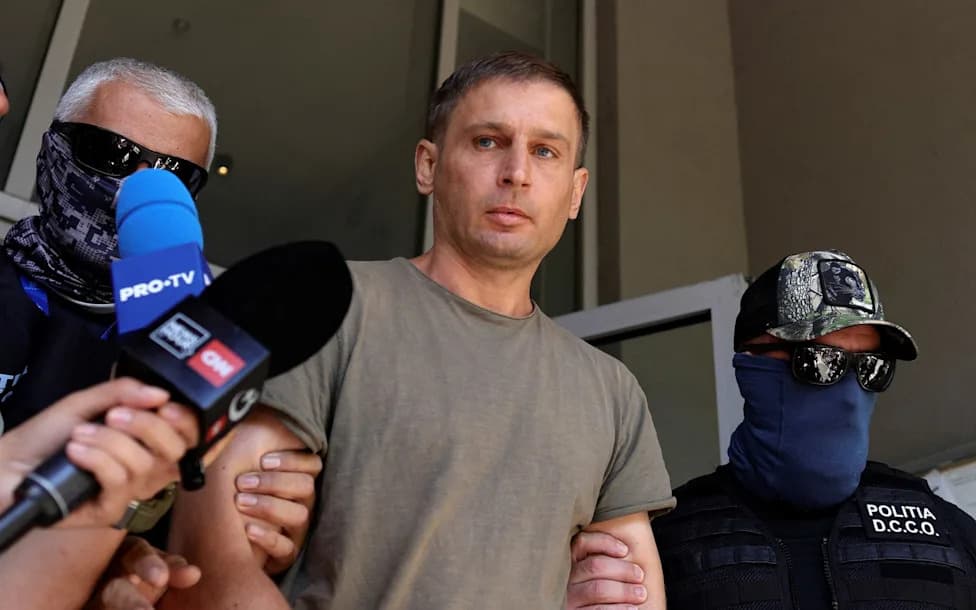
Denis Obrezko, 36, arrested in Thailand last year, has appeared in Boston federal court charged with conspiring to access protected computers in connection with a large cyber espionage campaign. U.S. authorities say he allegedly aided a Russia-aligned group called Void Blizzard, which Microsoft identified in May 2025. The FBI tied Obrezko to cryptocurrency payments used to obtain a VPS and domain name used in attacks, and has identified at least 11 hacked U.S. companies.
Suspected Russian Hacker Arrested in Thailand Appears in U.S. Court Over Void Blizzard Cyber Campaign
FILE PHOTO: A man holds a laptop computer as cyber code is projected on him in this illustration picture created on May 13, 2017. REUTERS/Kacper Pempel/Illustration/File Photo
BOSTON, June 10 (Reuters) - A suspected Russian hacker arrested in Thailand last year has been brought into U.S. custody and charged with helping to facilitate a series of cyberattacks tied to a Russia-aligned group known as Void Blizzard.
Denis Obrezko, 36, made his initial appearance in federal court in Boston on Tuesday. He faces a charge of conspiring to commit unauthorized access to a protected computer and is being held without bond. The case is being prosecuted by the U.S. Department of Justice's National Security Division.
U.S. prosecutors allege Obrezko aided a large-scale cyber espionage operation that targeted organizations important to Russian government objectives. The Justice Department and a court-appointed lawyer for Obrezko did not immediately respond to requests for comment.
Group Identified by Microsoft
Microsoft identified Void Blizzard in a May 2025 report, describing it as a relatively new threat actor observed conducting cyber espionage against organizations relevant to Russian state interests. According to Microsoft, Void Blizzard has been active since at least April 2024 and primarily targeted entities in NATO member states and Ukraine across sectors including government, defense, transportation, media, healthcare and non-governmental organizations.
Allegations and Evidence
In an affidavit filed in the case, an FBI agent said Void Blizzard’s operations focused heavily on mass email harvesting across a wide range of U.S. business sectors. The court filing says the FBI has identified at least 11 U.S. companies that were hacked — a figure it believes represents only a portion of the group's victims.
Charging documents allege the FBI linked Obrezko to cryptocurrency transactions used to purchase a virtual private server (VPS) and a domain name that were employed in attacks on companies in the United States and abroad.
(Reporting by Nate Raymond in Boston; Editing by David Gregorio)
Help us improve.