European law enforcement disrupted the KillSec ransomware group, arresting a 16-year-old suspected administrator in Alicante and seizing at least 110 TB of stolen data. Operation KillSwitch, led from Hamburg, targeted roughly 1,000 suspected attacks, about 500 of which were confirmed as successful, and prompted searches in four countries. A U.K. suspect, Fouad Eltibrizi ("Archduke"), faces a U.S. indictment and possible extradition. Investigators say KillSec used AI, exploited cloud vulnerabilities, and employed double-extortion tactics while demanding ransoms in cryptocurrency.
16-Year-Old Arrested in Spain Accused of Running KillSec Ransomware; Europol Seizes 110 TB of Stolen Data
Myriad: How high will Bitcoin go? Click to make your prediction.
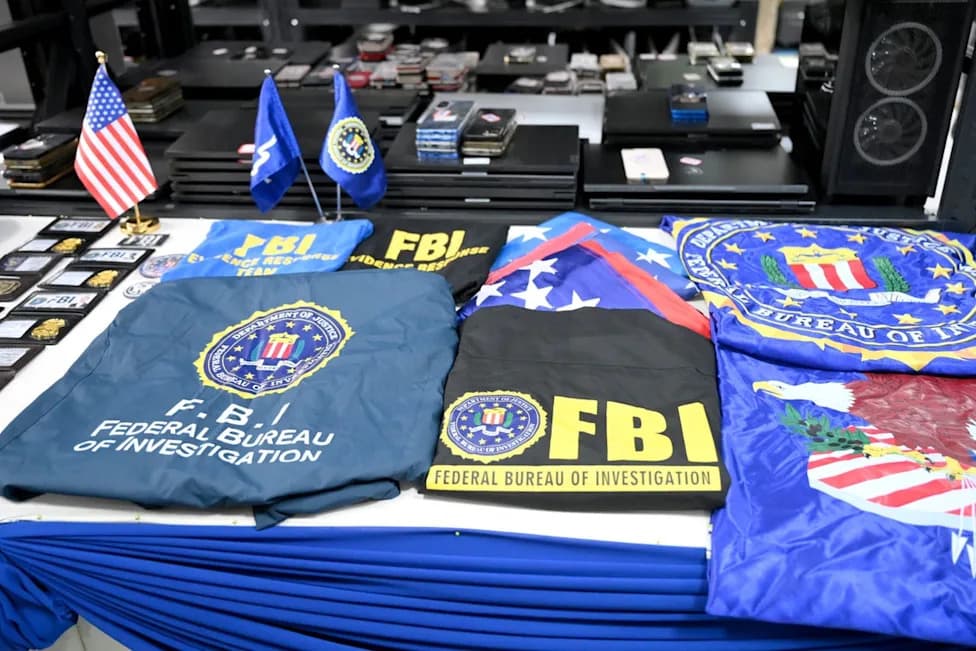
Spanish police have detained a 16-year-old Romanian national in Alicante suspected of being a principal administrator of the KillSec ransomware group, Europol said. Law enforcement across Europe simultaneously seized the gang's servers and leak site and secured at least 110 terabytes of stolen data.
Operation KillSwitch: Scope and Arrests
The action on September 30 was part of Operation KillSwitch, an investigation led by the Hamburg State Criminal Police Office and the city's public prosecutor into roughly 1,000 suspected attacks worldwide. Authorities have identified about 500 of those incidents as successful. As part of the operation, officers searched eight properties across Spain, Greece, Romania and the United Kingdom.
Two other suspects in their twenties were arrested — one in the U.K. and one in Romania — and a fourth individual, a developer who only recently turned 18 and was a minor when some alleged offences occurred, has been identified but not yet detained.
U.S. Indictment and International Coordination
One man arrested in Britain, identified by prosecutors as Fouad Eltibrizi (online handle: Archduke), was indicted by a federal grand jury in Puerto Rico on Sept. 16 on charges including conspiracy to access computers without authorization for financial gain, damaging protected computers and transmitting extortion threats. He was arrested within weeks and faces possible extradition to the U.S., where the indictment carries a maximum penalty of 10 years.
"Ransomware causes significant financial losses, operational disruption and harm to public confidence," said Detective Sergeant John Collinson of the Eastern Region Special Operations Unit.
How KillSec Operated
Europol said KillSec has been active since around 2024. The group exploited software vulnerabilities and poorly secured access points — particularly misconfigured cloud storage — to gain access to organizations' systems and copy internal files to infrastructure it controlled. Victims were publicly named on a dark web leak site and pressured with threats to publish data unless they paid. Where victims refused, some files were released for free download.
Authorities said KillSec used a double-extortion strategy: encrypting servers to disrupt operations while simultaneously threatening to publish stolen data if victims declined to pay because they had backups. Ransoms were frequently demanded in cryptocurrency. Swiss prosecutors have been investigating attacks on Swiss companies between October 2023 and June 2025 and opened a formal probe in July 2025.
Use of AI and Evidence Seizure
Investigators also found the group used artificial intelligence to build and maintain its ransomware infrastructure and to help identify potential victims. Five central servers are now under police control, multiple domains have been redirected to seizure notices, and officers are analysing seized devices while tracing proceeds — including cryptocurrency — with technical support from Europol's European Cybercrime Centre for crypto-tracing and digital forensics.
In the U.K., authorities have identified 28 victim companies; the Eastern Region Special Operations Unit arrested a 25-year-old suspected negotiator at an address in Levenshulme, Manchester.
Notable Alleged Breaches
U.S. prosecutors say KillSec posted a Puerto Rico breach on its leak site in March 2025 with samples of stolen patient data and a seven-day countdown. When the affected company did not meet demands, roughly 180 GB of patient records were published. The indictment also describes similar breaches in California, Washington State and Louisiana.
What Comes Next: Investigators continue forensic analysis of seized servers and devices, and international authorities are pursuing asset and cryptocurrency tracing and potential extraditions. The operation highlights continuing risks from poorly secured cloud systems, the growing use of AI by criminal groups, and the global nature of ransomware threats.
Help us improve.