Armenian cyber police raided a hotel office in Yerevan on July 23 after an intelligence-led probe into a group accused of impersonating U.S. freight carrier employees. The suspects allegedly diverted shipments, sold the goods and converted proceeds into cryptocurrency. Authorities seized equipment, described the scheme as organized and involving "particularly large amounts," and are working with unnamed U.S. law enforcement while searching for victims and related networks.
Yerevan Raid: Group Allegedly Posed As U.S. Freight Carriers, Diverted Shipments and Laundered Proceeds Into Crypto
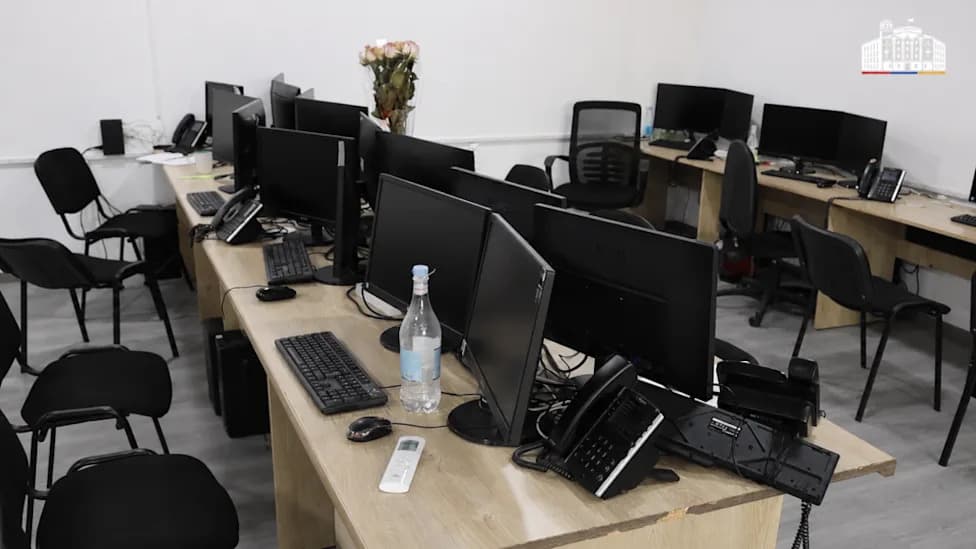
Computer workstations inside the Yerevan hotel space searched during a July 23 freight-theft investigation. (Photo: Armenian Interior Ministry)
Armenian cyber police raided a commercial office inside a Yerevan hotel on July 23 after a lengthy intelligence-led probe, authorities said on Aug. 14. Investigators allege the occupants posed as employees of U.S. freight carriers, redirected shipments entrusted to those carriers, sold the stolen goods and converted the proceeds into cryptocurrency.
The Interior Ministry said officers from the Criminal Police Cybercrime Department worked with the Investigative Committee to execute a surprise search and seize material described as important to an ongoing criminal inquiry. Authorities also released video footage of the July 23 operation.
Investigators reported that the group operated from the hotel using specialized computer equipment and software. Officials identified suspected members and assigned roles before the raid, characterizing the activity as an organized scheme involving thefts of what the ministry called "particularly large amounts," though no monetary total was provided.
According to a translated ministry statement, members of the alleged organization represented themselves as staff of companies that transport freight within the United States. By presenting that false identity, they gained the trust of brokers and shippers, then diverted shipments to alternate locations instead of completing intended deliveries. The suspects reportedly sold the cargo and moved funds into accounts controlled by members, which were later exchanged for various crypto assets.
Officials did not name any banks, specific cryptocurrencies, account holders or explain how blockchain or banking traces were followed. The Armenian Investigative Committee opened criminal proceedings after receiving a report about the suspected scheme and said its cybercrime investigators are cooperating with unnamed U.S. law enforcement partners to gather further evidence and identify any related networks operating inside Armenia.
Police said they continue searching for individuals and businesses that may have been targeted. The ministry withheld the number of intercepted shipments, the count of suspects involved and whether arrests have been made. It also did not identify the U.S. carriers the group purported to represent or disclose freight origins, pickup points or destinations.
Industry implications
Law enforcement and industry observers say the case illustrates how organized networks can orchestrate cargo theft from remote offices by exploiting trust in carrier identities before a physical pickup occurs. One industry commentator recommended implementing standardized fraud checks to verify a carrier's business controls, banking relationships and the identities of people involved — for example through Certified Fraud Compliance Officer training — to shift the focus from whether something merely seems suspicious to whether everything has been confirmed.
The inquiry is ongoing. Authorities have emphasized they are still gathering evidence and seeking to identify victims and any similar groups operating in the region.
Help us improve.