The U.S. military has disabled mobile advertising IDs (MAIDs) on government-issued devices after reporting showed commercially sold location data was used by Iran and other adversaries to monitor U.S. bases and personnel. A letter from Sen. Ron Wyden and Rep. Pat Harrigan asks the DoD inspector general to review policies and determine whether personal devices are the main source of leaked data. Experts say turning off MAIDs closes a major tracking loophole, but personal phones and preexisting commercial datasets remain significant OPSEC risks.
U.S. Military Disables Mobile Ad Trackers on Government Devices After Reports of Foreign Location Tracking
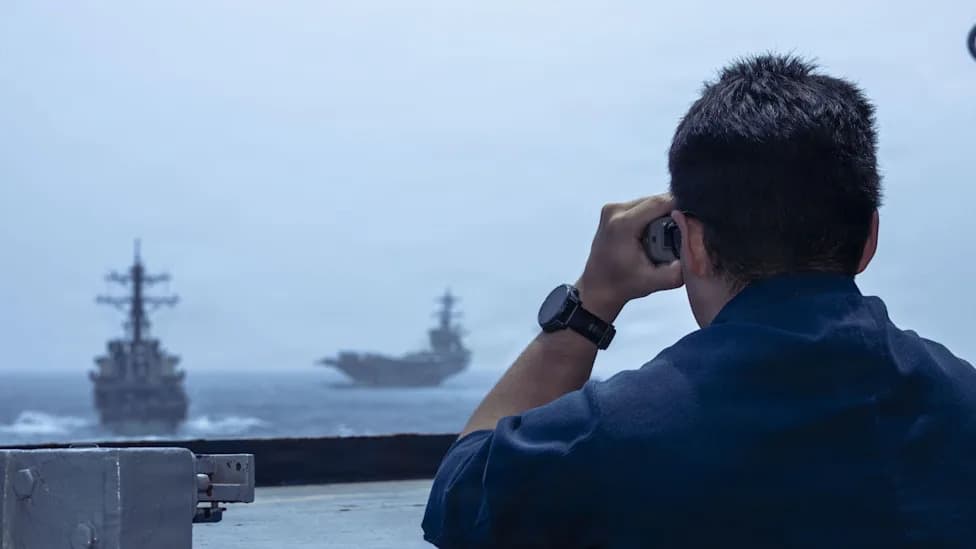
A sailor tracks other ships from the Arleigh Burke-class destroyer USS Milius in the Arabian Sea.
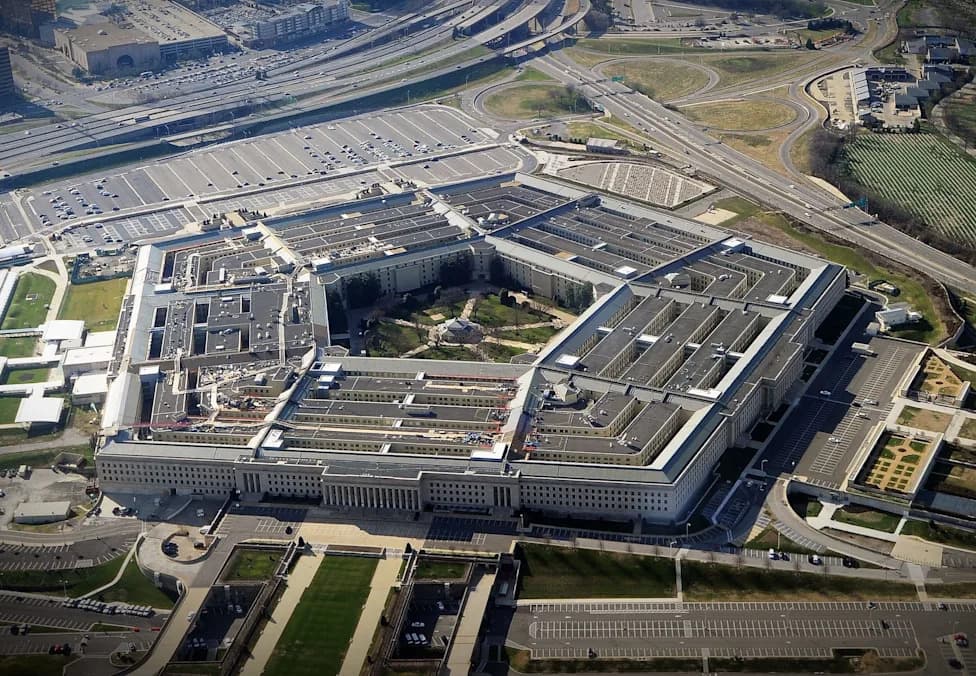
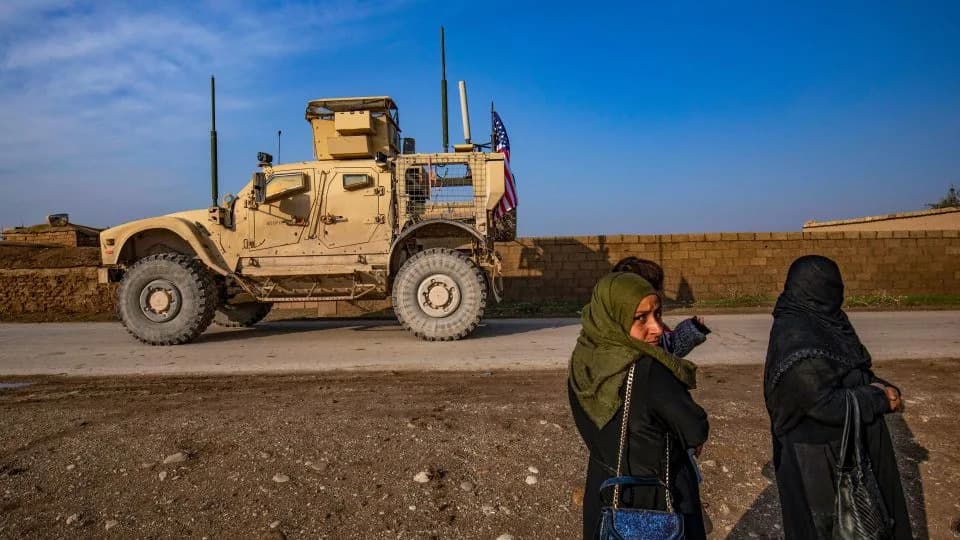
The U.S. military has disabled mobile advertising–tracking tools on government-issued phones, computers and other devices after reporting showed commercially available location data was being used by Iran and other adversaries to monitor and, in some cases, target American bases and personnel.
The disclosures appear in a letter shared with Congress by Sen. Ron Wyden (D-Ore.) and Rep. Pat Harrigan (R-N.C.). The lawmakers urged the Department of Defense Office of the Inspector General to review DoD security guidelines and assess ongoing vulnerabilities tied to commercial data collection.
Which Services Acted—and When
According to the letter, the Army, Navy, Air Force, Marine Corps and U.S. Special Operations Command confirmed they have disabled Mobile Advertising IDs (MAIDs) on government-issued devices. Some branches only implemented the changes this summer; the Air Force told members of Congress it ordered ad trackers disabled in July.
What Are MAIDs And Why They Matter
Mobile Advertising IDs, or MAIDs, are unique identifiers tied to individual devices. Mobile apps commonly collect MAIDs and other metadata that can reveal device location, habitual routes and routines—information that can be aggregated, bought from data brokers and exploited by foreign actors.
"The sale of location data, particularly that of U.S. government personnel, poses a serious threat to national security," Sen. Wyden wrote in the correspondence.
Eva Galperin, Director of Cybersecurity at the Electronic Frontier Foundation, called disabling MAIDs "a very simple and straightforward way that you can close a loophole," while noting MAIDs are a major but not the only tracking method.
Ongoing Risks: Personal Devices And Existing Data
Lawmakers and cybersecurity experts emphasize that turning off MAIDs on government-issued equipment reduces an important attack surface but does not eliminate risk. Personal phones and wearable devices used inside bases or in operating areas continue to generate location data. Wyden and Harrigan asked the inspector general to determine whether personal devices are the primary source of leaked location information and, if so, to recommend concrete policy and technical controls to protect personnel and operational security (OPSEC).
U.S. Central Command (CENTCOM) has tightened cybersecurity guidance since late last year and has warned troops that Iran has used photos, video and other cellphone content to assess the effects of attacks. The Department of the Navy also recently alerted sailors and Marines to a "coordinated, multi-domain campaign" targeting service members through their digital footprints and urged personnel to obscure online ties to the military.
Galperin noted that previously collected commercial datasets—compiled and sold before MAIDs were disabled—could still be useful to adversaries, though they lack the real-time updates that active tracking provides. The larger operational risk remains the persistent use of personal devices in sensitive areas.
What Comes Next
The DoD Office of the Inspector General is being asked to review policies, identify whether personal devices are the main leak vector, and, if necessary, recommend enforceable technical controls, updated guidance for deployed personnel, and other measures to protect DoD personnel from commercial surveillance.
Bottom line: Disabling MAIDs on government devices is an important, straightforward mitigation. But comprehensive OPSEC will require curbing personal-device exposures, addressing previously sold data, and implementing clearer, enforceable controls.
Help us improve.