Revelations that cameras on Royal Navy K3 Scout drones sent "heartbeat" signals to an IP address in China highlight vulnerabilities in complex, international defence supply chains. The MoD and Kraken say no sensitive data was transmitted, and the devices reportedly complied with US NDAA rules. Still, the episode echoes prior concerns—such as the SBS ban on Chinese electric cars and the Huawei telecoms ban—and argues that the UK must accelerate efforts to diversify suppliers, tighten oversight and secure critical systems.
Britain Must Not Be Complacent About China: Drone Cameras That Pinged A Chinese IP Expose Supply-Chain Risk
iStockphoto
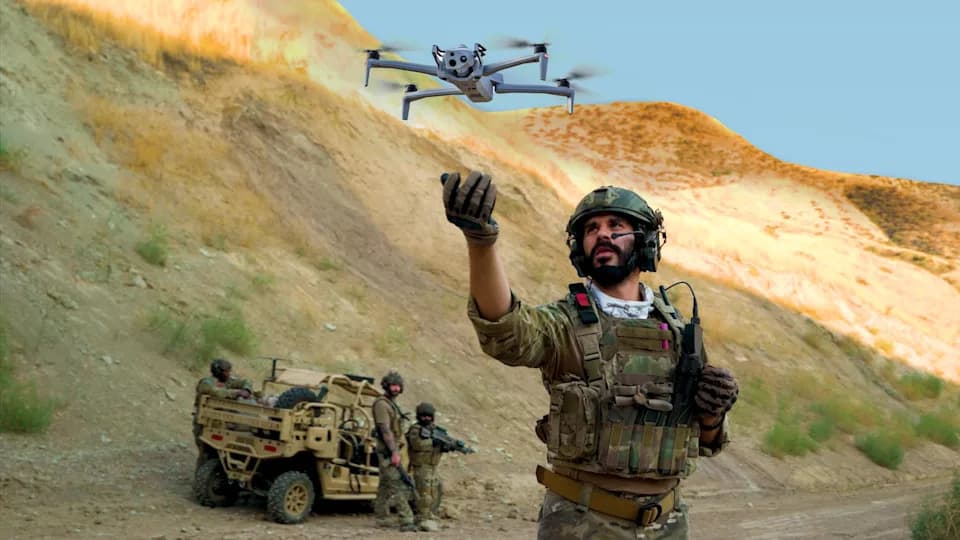
Military technology is evolving fast, and Britain’s armed forces cannot afford to fall behind as battlefields become increasingly populated by artificial intelligence and unmanned systems. The Telegraph’s report that cameras fitted to the Royal Navy’s new K3 Scout surveillance drones sent signals to an IP address in China should act as a clear warning to planners, commanders and procurement officials.
What Happened
Cameras installed on vessels used by the Royal Marines and the Special Boat Service (SBS) reportedly transmitted so‑called “heartbeat” signals confirming the devices were online and functioning to an IP address in China. The Ministry of Defence and Kraken Technology Group, the British defence contractor that sourced the parts, have both said that no sensitive operational data was transferred abroad. The components were reportedly compliant with the US National Defense Authorization Act (NDAA) rules that bar blacklisted Chinese manufacturers.
Why This Matters
That reassurance is limited comfort. Defence supply chains are highly complex and internationalised, and even components that meet regulatory compliance can present security risks if they phone home, contain hidden functions, or rely on remote services hosted overseas. China is an increasingly assertive global power, and successive officials and analysts have warned about vulnerabilities in a wide range of Chinese‑made goods. Earlier concerns have prompted actions such as the SBS ban on Chinese‑made electric cars at its headquarters and the UK’s 2020 decision to remove Huawei equipment from national telecoms infrastructure by 2027.
What Should Be Done
Fully securing military supply chains cannot be achieved overnight, especially where alternative suppliers for specialised components are limited. Nonetheless, government and industry should accelerate practical steps to reduce exposure, including stronger supplier vetting, mandatory firmware and network audits, contractual requirements for data sovereignty, diversification and onshoring of critical components where feasible, and robust real‑time monitoring that isolates sensitive systems from external services.
Bottom Line: The incident highlights persistent vulnerabilities in modern defence procurement and underlines the need for faster, more decisive action to protect operational security and ensure the UK’s armed forces remain technologically resilient.
Help us improve.